

How Magisk Achieves Systemless Root Without Modifying System Partitions
Rooting used to mean rewriting your phone from the inside. You flashed a zip, it wrote a binary into the system partition, changed permissions on a handful of core files, and left a trail any integrity check could follow. I rooted phones that way for years, and every system update became a small crisis: restore the stock system, take the update, root again, hope nothing broke. Magisk changed that bargain completely. It gives apps root access while the system partition stays byte-for-byte identical to the version your manufacturer shipped.
The trick is not magic, and it is not a cheat code. It is a careful piece of boot-time engineering. Magisk patches the boot image, starts its own code before Android finishes starting, and lays a virtual layer over the system. Apps see the files Magisk wants them to see. The disk underneath never changes. When you remove Magisk, the layer disappears and the phone is back to stock, with no leftover edits in the system partition to clean up.
This guide walks through that mechanism in plain language, with enough technical detail that you can actually follow what happens at each stage. You will see how boot image patching works, what the ramdisk does, how the overlay is built, why mount namespaces matter, what Zygisk does inside app processes, and where the whole design still has limits. If you have ever wondered why Magisk survives in a way older root methods never did, the answer is in these layers.
What Systemless Root Really Means for Your Android Phone
Systemless root means root access without writing to the system partition. The system partition, usually mounted at /system, holds the operating system files: frameworks, system apps, libraries, fonts, and configuration. On a modern phone it is mounted read-only during normal use, and on many devices it is protected by verified boot, which checks its contents against a signed hash tree before Android starts. Writing to it breaks that verification, and that is exactly what older root methods did.
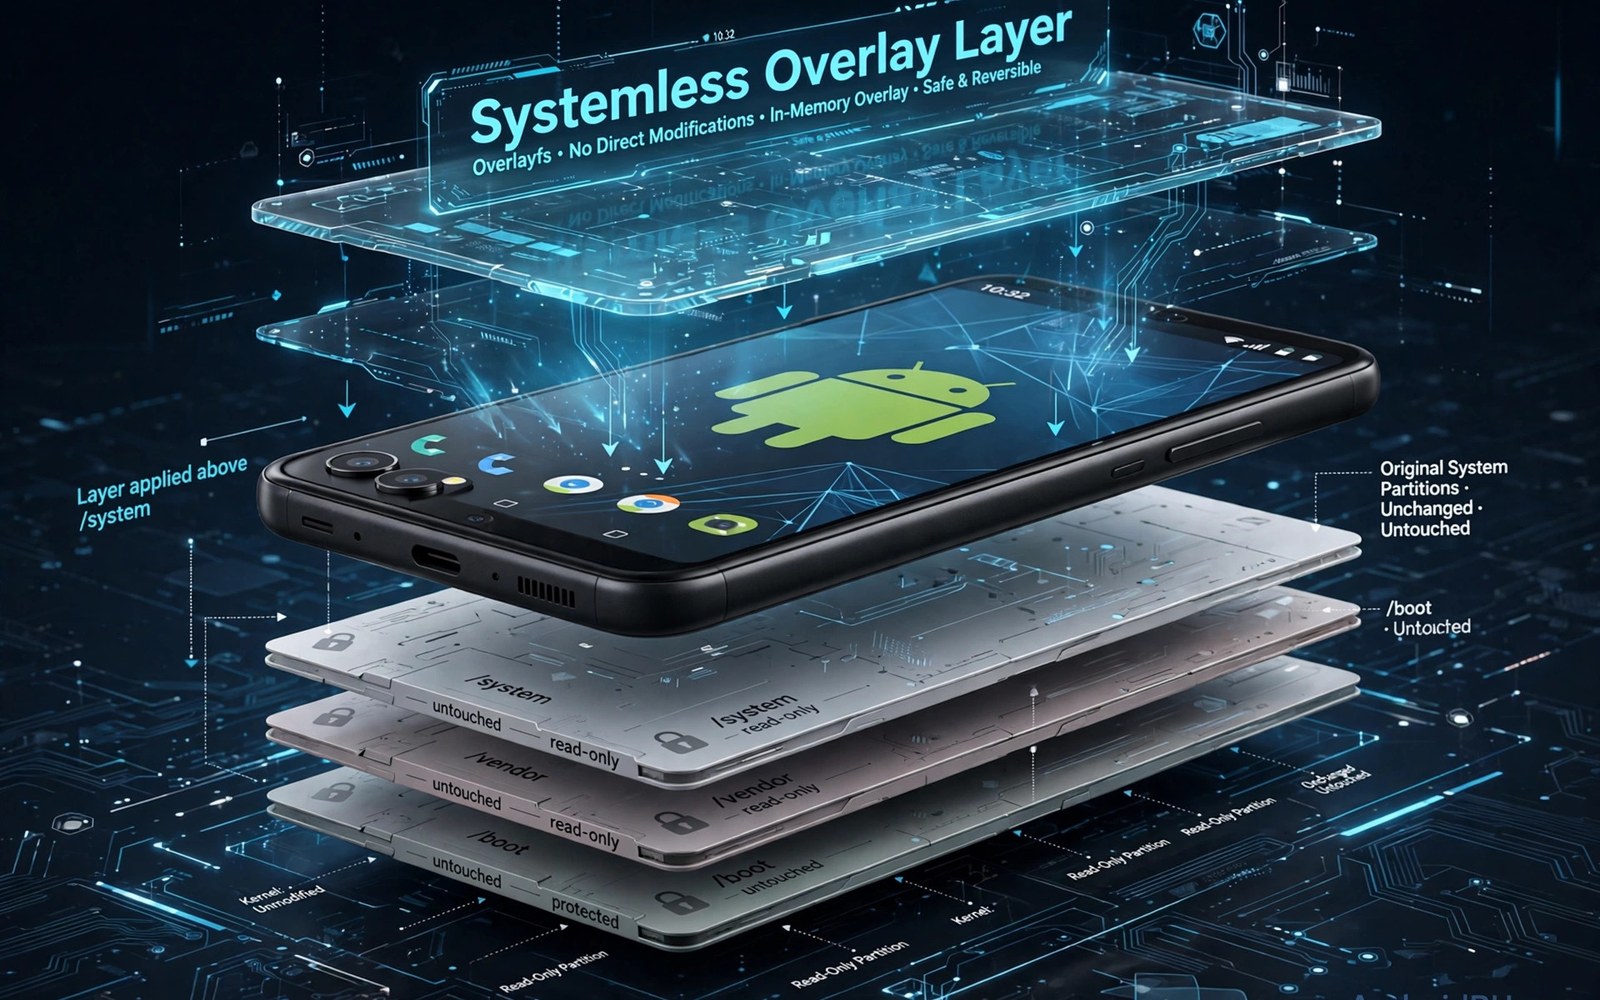
Magisk takes a different route. It leaves /system alone on disk and changes what the running system sees instead. Think of it like placing a clear sheet over a printed page and writing on the sheet. A reader sees your writing together with the printed text, but the page underneath is untouched. Peel the sheet away and the original page is exactly as it was. That sheet is the overlay Magisk builds at every boot, and it is rebuilt fresh each time the phone starts.
That distinction matters for three practical reasons. First, uninstalling Magisk is clean: restore the stock boot image and there is nothing left to undo in the system partition. Second, system updates are less destructive, because the update can replace system files without fighting a modified partition. Third, integrity checks that scan the system partition find nothing changed, because nothing was changed. That last point is often misunderstood, so it deserves a straight answer: systemless root reduces the footprint, but it does not make a phone invisible to every check. Apps can still look for the manager app, watch for known processes, or rely on hardware attestation that flags a modified boot image. Magisk hides the system edits. It cannot hide the fact that the boot image was patched.
How systemless root differs from the old system root method
The old method, often called system root, installed the su binary directly into /system/xbin or /system/bin and set its permissions so apps could call it. It sometimes replaced the app_process binary or edited build.prop as well. Every one of those edits lived on disk, in the partition that verified boot checks. A factory reset removed user data but the system edits stayed, and an over-the-air update often failed outright because the update script found files it did not expect.
Systemless root flips the storage question. Nothing root-related lives in /system at all. The Magisk binaries, the module files, and the superuser daemon all live in the boot image ramdisk area or in the data partition, and they are mounted into place at boot. The system partition keeps its original hash, verified boot of the system partition still passes, and the phone can take an update that replaces system files without tripping over root leftovers.
Why leaving the system partition alone makes updates and removal safer
I learned this the practical way on a phone I used as a daily driver for two years. With the old method, every monthly security patch meant a full evening: flash stock system, take the update, re-root, reinstall modules, reconfigure everything. With Magisk, the same update meant patching the new boot image and flashing it, and the modules and settings carried over from the data partition. The work shrank from an evening to about fifteen minutes.
Removal is just as clean. Flash the stock boot image back, and the phone is stock as far as the system partition is concerned. There is no need to reflash a full factory image to scrub root traces out of /system, because root never wrote there. That is the single biggest quality-of-life difference between the two approaches, and it is the reason Magisk became the standard root method on modern Android.
The three places Magisk actually stores its files
Magisk keeps its working files in three places, and none of them is the system partition. The early boot code lives in the patched boot image, inside the ramdisk or the boot image itself on newer devices. The Magisk app and its settings live in the data partition, under the app data directory, where they survive a system update. Module files live in /data/adb/modules, also in the data partition, which is why your modules and their settings are still there after you flash a new patched boot image.
What verified boot still checks, and what it does not
Verified boot, through dm-verity and Android Verified Boot, checks the integrity of partitions such as system and vendor against signed hashes. Because Magisk does not touch those partitions, their checks still pass. The boot partition is a different story: Magisk patches it, so its hash changes, and a device with a locked bootloader will refuse to boot a patched image. That is why Magisk requires an unlocked bootloader. The phone trusts the bootloader to decide what may boot, and an unlocked bootloader permits the patched image while warning you at startup.
How Magisk Patches the Boot Image Step by Step
Everything starts with the boot image. On Android, the boot image is the file the bootloader loads first. It contains the kernel and, on many devices, a ramdisk: a small filesystem loaded into memory that holds the first scripts and binaries Android needs before the main system starts. Magisk modifies this image, not the system partition, and that one decision shapes the entire design.
The patching process itself is straightforward to describe, though the code behind it handles a long list of device differences. You start with the stock boot image for your exact phone model and exact build number. That match matters more than almost anything else in this guide. A boot image from a different build, even a nearby one, can fail to boot or can boot with broken drivers, because the kernel and the ramdisk are built for a specific software version.
Magisk unpacks that stock image, inserts its own early-boot code, repacks it, and writes out a patched file, usually called magisk_patched.img. You then flash that file to the boot slot with fastboot. From that moment, every boot runs Magisk code before Android finishes starting. The system partition is never involved in the install at all.
Getting the correct stock boot image for your exact build
The most common install failure I have seen is a mismatched boot image. The fix is boring but reliable: check Settings, About phone, and write down the build number, then get the factory image or firmware package for that exact build from your manufacturer. Extract the boot.img from it and keep both the stock and patched files on your computer, labelled with the build number and the date. I keep mine in a folder named after the phone and the build, because a folder called magisk_patched.img with no label is a trap waiting for the next update.
On some phones you can also pull the boot image from the device itself, but the factory image route is the one I recommend to anyone doing this the first time. It gives you a known-good stock file you can flash back to if anything goes wrong, and that safety net is worth the extra download.
What the patcher adds inside the image
The patcher inserts a small init replacement and a set of Magisk binaries into the ramdisk. The key piece is magiskinit, which runs as the first process, PID 1, in place of the normal init during the earliest stage of boot. Running that early is what gives Magisk control over everything that follows: it can set up mounts, start the superuser daemon, and hand over to the real init once its own setup is done. On devices without a separate ramdisk in the boot image, newer Magisk versions place the code in the boot image itself or use the vendor boot image, and the patcher detects which layout your device uses.
Alongside magiskinit, the patch adds the magisk binary, the magiskpolicy tool that adjusts SELinux rules, and the scripts that load modules. The patched image is usually close in size to the stock image. A patched file that is far smaller than stock, or only a few kilobytes, almost always means the patch failed or the input file was wrong. Checking the size before flashing is a thirty-second habit that saves a bootloop.
Flashing the patched image to the right boot slot
Most modern phones use A/B boot slots: two copies of the boot partition, called slot A and slot B. One slot is active and the other waits for updates. When an update arrives, it writes to the inactive slot and the phone boots from it next time. You must flash the patched image to the slot the phone will actually boot from. Check the active slot with fastboot getvar current-slot before flashing, then flash with fastboot flash boot magisk_patched.img, or fastboot flash boot_a or boot_b if your device needs the slot named explicitly. Flashing the inactive slot is one of the classic reasons root seems to vanish after a reboot.
Verifying the patch before you reboot
Before rebooting, compare the patched file size with the stock file, confirm the slot, and keep a terminal window open with the stock image path ready. If the phone fails to boot, you can flash the stock image back in under a minute. Writing the restore command down before you flash, instead of searching for it while the phone sits on a logo screen, turns a stressful moment into a routine one.
adb push magisk_patched.img /sdcard/
adb reboot bootloader
fastboot getvar current-slot
fastboot flash boot magisk_patched.img
fastboot reboot
The commands above are the standard flow for a phone with a normal boot partition layout. Some devices need the vendor boot image patched instead, or need the image flashed to a named slot. When a step looks different for your model, follow the device-specific instructions for that model rather than forcing the generic flow.
The Ramdisk, Early Mount, and the Magic Mount Overlay
The ramdisk is a small filesystem that the kernel loads into memory at boot. It holds the early init scripts, the first binaries, and the configuration Android needs before the real system partition is mounted. Because it runs before apps, before most services, and before the system partition is fully up, code placed in the ramdisk gets the first word on how the system will look. That early position is the whole reason Magisk lives there.
When a Magisk-patched phone boots, magiskinit runs first. It mounts the partitions it needs, reads the Magisk configuration from the data partition, and then performs the step Magisk calls magic mount. Magic mount is the overlay mechanism: for each file a module wants to replace, Magisk creates a bind mount that shows the module file at the system path, while the original file stays untouched on disk. For files nobody replaces, the system simply reads the original. The result is a merged view, built entirely in memory at boot, with no writes to the system partition.
Here is the catch, and it is an honest one: the overlay only exists while the phone is running. It is not stored anywhere permanent. That is a feature, not a bug. A bad module cannot permanently damage the system partition, because its changes vanish the moment you disable the module and reboot. It also means the overlay must be rebuilt at every single boot, which is why Magisk code has to run so early.
Bind mounts and mirrors explained in plain language
A bind mount is a Linux feature that makes one directory or file appear at a second location. If you bind-mount /data/adb/modules/myfont/system/fonts/Roboto.ttf over /system/fonts/Roboto.ttf, every app that opens the system font path reads the module file instead. The original font file is still on disk in the system partition, unchanged, but nothing can see it through that path while the mount is active. Magisk uses this trick file by file, only for the paths modules actually replace.
For whole directories, Magisk uses mirrors. It mounts a mirror of the real system at a hidden path, then builds the visible system view from a combination of the mirror and the module files. This lets a module add a new file to a system directory, or replace one file in a directory of hundreds, without copying the rest. The untouched files still come from the real system, which keeps the overlay light and keeps the phone stable.
What happens to the overlay when you remove a module or Magisk itself
Disable a module in the Magisk app, reboot, and its bind mounts are simply not created. The system paths show the original files again, as if the module had never been there. Uninstall Magisk entirely and flash the stock boot image, and even the mount setup code is gone. There is nothing to scrub from the system partition, because nothing was ever written there. That clean removal is the practical payoff of the whole systemless design, and it is the reason testing a new module feels low-risk compared with the old days of editing system files directly.
Why the overlay is rebuilt at every boot
Mounts do not survive a reboot. They live in the kernel mount table, which is created fresh each time the phone starts. Magisk therefore repeats its setup on every boot: magiskinit runs, reads the module list, creates the mirrors and bind mounts, starts the daemon, and hands over to normal init. If a module causes a bootloop, that fresh rebuild is also your rescue path. Magisk can detect repeated failed boots and enter a safe mode with modules disabled, or you can disable modules from recovery, because the next boot simply builds the overlay without them.
Mount Namespaces and Why Apps See a Different System
Mount namespaces are the second half of the hiding story, and they are easy to misunderstand. A mount namespace is a Linux feature that gives a process its own private view of mounted filesystems. Changes made inside one namespace do not affect processes in another namespace. Android gives each app its own mount namespace, and Magisk uses that isolation to control what each app can see.
In practice, this means Magisk can build a slightly different view of the filesystem for different apps. The Magisk daemon runs in the global namespace, where it sets up the overlay. When an app starts, it inherits a namespace that includes the overlay, but Magisk can also unmount its own traces inside the namespace of an app on the denylist. That app then sees a filesystem that looks like a stock phone, while a root app in a different namespace still sees the Magisk files it needs. The disk is the same for everyone. The view is not.
This is clever, and it is also limited. Mount namespace tricks hide files, but they do not hide everything. An app can still check for the Magisk app package, look at process lists, test for root binaries through other paths, or ask the hardware to attest the boot state. A denylist entry helps with apps that do a simple filesystem check. It does not defeat hardware attestation, and no mount trick ever will, because attestation checks the boot image itself, not the files the app can see.
How the denylist uses namespaces to hide Magisk traces
When you add an app to the denylist in the Magisk app, Magisk records that package name. The next time that app starts, Magisk unmounts the Magisk-specific mounts inside that app namespace before the app code runs. The app sees the normal system files, no Magisk binary in its path, and no module overlays. The app still runs on a phone with a patched boot image, but the traces it would normally find by looking at the filesystem are gone from its view.
That is why the denylist sometimes works and sometimes does not. An app that only checks for files or the su binary will pass. An app that uses Play Integrity or hardware-backed attestation will still see that the boot image is modified, because that check happens outside the app namespace, at the hardware level. Knowing which kind of check an app uses saves a lot of frustration: if a banking app fails after denylist and a renamed manager app, the cause is usually attestation, and no further hiding setting will fix it.
Why namespace hiding cannot beat hardware attestation
Hardware attestation asks the phone security hardware whether the boot chain is in a verified, locked state. A patched boot image on an unlocked bootloader fails that question no matter what the filesystem looks like. Mount namespaces control what an app sees when it opens a file. They have no influence on what the security chip reports about the boot image. This is a hard limit of the systemless approach, and anyone who promises a way around it for every app is selling a shortcut that does not exist.
How the Magisk Superuser Daemon Handles Root Requests
Root access in Magisk is not a free-for-all. It is a managed service run by the Magisk daemon, magiskd, which starts during early boot and listens for requests from apps. When an app wants root, it does not get to run as root directly. It calls the su binary, which forwards the request to the daemon, and the daemon decides whether to allow it based on the rules you set in the Magisk app.
That prompt you see, asking whether to grant root to an app, is the daemon doing its job. You can allow once, allow permanently, or deny. You can review the log of past grants, revoke access for an app you no longer trust, and set a timeout so a grant expires. Good habits here protect your data more than any hiding feature ever will, because a careless grant hands an app full control of the phone.
The daemon also handles the practical details: it sets up the mount namespace for the requesting app, makes sure the app sees the overlay it needs, and logs the request so you can audit it later. It runs as a privileged process, separate from the apps it serves, which is why a crashing app cannot take the root service down with it.
Granting, denying, and auditing root access per app
Open the Magisk app, go to the superuser section, and you will see every app that has asked for root, with its current rule. My own rule is simple: grant root only to apps I installed deliberately for a specific job, deny everything else, and review the list once a month. A file manager that needs root to edit a config file is a reasonable grant. A random game that asks for root on first launch is not, and the correct answer there is a permanent deny.
The log matters too. If an app you barely use suddenly requests root after an update, that is worth a look before you tap allow. The daemon records the time and the requesting process, so you can spot a change in behaviour instead of guessing.
What to do when a root request is denied or times out
A denied request usually means the rule for that app is set to deny, or the app is calling su in a way the daemon does not recognise. Check the superuser list first, change the rule to ask again, and retry. A request that times out with no prompt often means the Magisk app itself is frozen, battery-optimised into silence, or the daemon did not start. Reboot, check that the Magisk app opens normally, and test with a single trusted root app before blaming the app that failed.
Zygisk and How Modern Magisk Modules Inject Code
Zygisk is the modern way Magisk modules run code inside apps. To see why it exists, you need to know what Zygote is. Zygote is the parent process for Android apps: when you open an app, the system forks a copy of Zygote, loads the app code into it, and that copy becomes the app process. Zygisk injects module code into Zygote itself, so every app forked from it can carry the module code from the very start.
That early injection is powerful. A module can change how an app behaves, add a feature, or hide a trace, without editing the app files and without touching the system partition. It works through the same systemless idea as everything else in Magisk: the code is loaded at runtime, from files in the data partition, and it disappears when the module is disabled.
It is also the part of Magisk most likely to cause an app crash, because the injected code runs inside every app process unless the module says otherwise. A good Zygisk module checks which app it is running in and does nothing in apps where its tweak makes no sense. A careless module injects into everything, and the result is random crashes in apps that have nothing to do with the module. When a new module starts crashing apps, disabling Zygisk is the fastest way to test whether injection is the cause.
How Zygisk replaced the older injection framework
Before Zygisk, Magisk used an older injection framework called Riru, which hooked into Zygote through a different mechanism. Riru worked well for its time, but it needed maintenance for each Android version and it had its own detection footprint. Zygisk replaced it by building the injection directly into Magisk, with a cleaner interface for module authors and better behaviour on modern Android versions. If you are following a guide written before 2022 and it tells you to install Riru, stop and find a current guide: mixing the old framework with a modern Magisk version is a reliable way to break a working install.
For users, the practical difference is simple. With Zygisk, you enable it in Magisk settings, install Zygisk modules, and reboot. The modules load automatically into app processes. With the old framework, you installed a separate module first and hoped it matched your Android version. Zygisk removed a whole layer of version matching, which is one reason modern Magisk feels more stable than the versions from a few years ago.
When to disable Zygisk to fix app crashes
Here is the troubleshooting order I use when apps start crashing after a module change. First, disable Zygisk in Magisk settings and reboot. If the crashes stop, a Zygisk module is the cause. Then re-enable Zygisk and disable the Zygisk modules one at a time until the crash returns, which identifies the culprit. If the crashes continue with Zygisk off, the cause is a different module or the base install, and you move on to disabling modules in groups. This separation between root access and injection is a genuine help: root keeps working without Zygisk, so you can test one layer at a time.
What Zygisk modules can and cannot change
Zygisk modules can change app behaviour at runtime, intercept calls, and adjust what an app sees. They cannot change the system partition, because nothing in Magisk can, and they cannot fake hardware attestation, because that check happens outside the app process. A module that promises to make every banking app work by hiding root is promising something the architecture does not support. The honest modules say which apps they target and what they actually change, and those are the ones worth keeping.
Magisk Modules Without Touching System Files
Modules are the reason many people root in the first place. A module is a package of files and scripts that Magisk mounts over system paths at boot, using the same overlay mechanism described above. A font module replaces font files. An audio module replaces audio configuration and libraries. A system tweak module changes a setting file. In every case, the original files stay on disk, and disabling the module removes its overlay at the next boot.
This design makes testing a module far safer than the old way of editing system files. You can install a module, reboot, try it for a day, and remove it cleanly if you do not like it. You do not need to restore a full system image to undo a bad module. You can even disable all modules from recovery if a module causes a bootloop, because the next boot simply builds the overlay without them.
That safety has a limit worth stating plainly. A module cannot damage the system partition, but it can still crash the phone, break an app, or drain the battery. The overlay protects the disk. It does not protect the running system from bad code. Module quality matters just as much as the systemless design, and the source of a module matters more than its description. Install modules from their official release page or a repository you trust, and be careful with random files shared in chat groups.
How a module is structured and loaded at boot
A Magisk module is a zip file containing a module.prop file with its name and version, a system folder with the files it wants to overlay, and optional scripts that run at boot or when the service starts. When you install it, Magisk extracts it to /data/adb/modules, and on the next boot the mount setup reads that folder and creates bind mounts for every file inside the system folder. A file at system/fonts/Roboto.ttf inside the module appears at /system/fonts/Roboto.ttf in the running system.
Modules can also include a post-fs-data script that runs early, before the system finishes mounting, and a service script that runs later, once the system is up. Those scripts let a module do more than replace files: it can change a setting, start a service, or adjust a value at boot. That power is why a bad script can cause a bootloop even though no system file was changed.
Testing a new module without risking your daily phone
My routine for a new module is deliberately slow. Install one module at a time, reboot, and use the phone normally for a full day before installing the next one. If something breaks, I know which module did it. Installing five modules at once and then debugging the result is a waste of an evening, and it is the most common self-inflicted problem in Magisk troubleshooting. One module, one day, then the next.
Recovering from a bad module with safe mode and recovery
Magisk watches for repeated failed boots. After several failures it enters a safe mode with modules disabled, so the phone can boot and you can remove the bad module from the Magisk app. If safe mode does not trigger, you can disable modules from a custom recovery, or use the Magisk app in recovery mode on supported devices. Keep a recovery tool ready before you test new modules, not after a bootloop has already happened.
Updates, OTA Survival, and Troubleshooting Common Magisk Problems
System updates need care on a Magisk phone, because an update usually replaces the boot image. When the new boot image arrives without the Magisk patch, root disappears at the next boot. The system itself is fine, and your modules are still in the data partition, but the early boot code that sets up the overlay is gone. The fix is to patch the new boot image and flash it, which restores root without touching your apps or settings.
There are two common ways to handle this. The careful way is to restore the stock boot image, take the over-the-air update, then patch the new boot image from the updated firmware and flash it. The faster way, on devices that support it, is to use the update flow inside the Magisk app, which patches the inactive slot before the update switches to it. Both work. The right choice depends on your phone and the update type, and the wrong choice usually costs you a bootloop rather than data, because the system partition is untouched either way.
Whatever method you use, keep a copy of the stock boot image for your current build and a copy of the patched image, labelled with the build number. Mixing images from different builds is one of the fastest ways to a phone that will not boot, and clear labels are the cheapest insurance against it.
Bootloop after a module install
A bootloop after installing a module is the most common Magisk problem, and it is also the most recoverable. Let the phone fail to boot a few times so safe mode can trigger, then open the Magisk app and remove the last module you installed. If safe mode does not trigger, boot into recovery and disable modules from there. Removing the last module usually restores boot, because the overlay is rebuilt without it on the next start.
Root loss after a system update
Root loss after an update almost always means the update replaced the patched boot image with a stock one. Reflashing the patched image for the new build restores root in most cases. If you do not have a patched image for the new build yet, extract the boot image from the new firmware, patch it in the Magisk app, and flash it. Keep the patched image labelled by build number, because the next update will ask for the same routine again.
Manager app detection and denylist limits
Some apps scan for the Magisk manager app by its package name. Renaming the manager app to a random name in Magisk settings makes that simple scan harder, and the denylist hides filesystem traces from the apps you add to it. Together these steps help with apps that do basic checks. They do not help against hardware attestation, and some apps will stay blocked no matter what you change. Accepting that limit early saves a lot of time spent chasing a hiding trick that cannot work for that app.
Module conflicts that look like app bugs
Two modules can try to change the same file, and the result looks like an app bug: a crash, a missing feature, or a setting that will not stick. Disable modules in groups to find the conflict, then enable them one at a time until the fault returns. The module that brings the fault back is the one conflicting with the rest, and the fix is usually to keep only one of the two.
A short pre-flash checklist that prevents most failures
Check the build number matches the boot image. Check the active slot. Check the patched file size against stock. Keep the stock image path written down. Test root with one trusted app after boot, then run a full day without modules before adding them back. That short list prevents the failures I see most often, and it takes less than five minutes.
For a fuller picture of the install chain, read about what Android rooting means and why people choose it before you start, and study how boot image patching installs root access alongside this guide. If you are weighing other approaches, compare Magisk with an alternative kernel patching root method and choose based on your phone and your goals, not on which method is newest.
| Method | System partition | Modules | Detection risk |
|---|---|---|---|
| Magisk systemless | Untouched on disk | Large ecosystem, Zygisk | Boot image patch is detectable by attestation |
| Old system root | Modified directly | Limited, no overlay | High, files visible in system |
| Kernel patching | Untouched on disk | Smaller ecosystem | Kernel change is detectable by attestation |
Frequently Asked Questions About Magisk Systemless Root
What does systemless root mean in practice?
It means root access without writing to the system partition. Magisk patches the boot image, builds an overlay of bind mounts at boot, and apps see the merged view while the real system files stay unchanged on disk. Removing Magisk restores the stock boot image and the overlay disappears.
How does Magisk hide root from apps that check for it?
Magisk hides filesystem traces using mount namespaces and the denylist, and you can rename the manager app to avoid package-name scans. These steps help against simple checks. They do not defeat hardware attestation, which checks the boot image itself and cannot be hidden by changing what an app sees in the filesystem.
Why does root disappear after a system update?
An update usually replaces the patched boot image with a new stock one, so the Magisk early boot code is gone. Your modules and settings stay in the data partition. Patch the boot image from the new firmware and flash it to restore root.
Can a Magisk module damage the system partition?
No, a module cannot write to the system partition through the overlay, because the overlay only creates mounts in memory. A bad module can still crash apps or cause a bootloop, so install modules from trusted sources and test one at a time.
Is Zygisk required for Magisk root to work?
No. Zygisk is the injection layer for modules that run code inside app processes. Root access through the superuser daemon works with Zygisk disabled, and disabling it is a useful first step when a new module causes app crashes.
What to Do Next With Your Magisk Setup
If you take one thing from this guide, make it the boot image habit. Keep the stock image for your current build, keep the patched image labelled next to it, and check the active slot before every flash. That habit alone prevents most failed installs, most lost-root surprises after updates, and most panicked searches for a stock image while the phone sits on a logo screen.
Then test the base install before adding modules. Boot with Magisk active and no modules for a full day. Check that root prompts work, that your banking apps behave as you expect, and that the battery and performance feel normal. Only then add modules one at a time. A stable base with a few good modules beats a phone loaded with twenty modules and a crash you cannot trace. Start with the boot image, prove the base, and build from there.

