

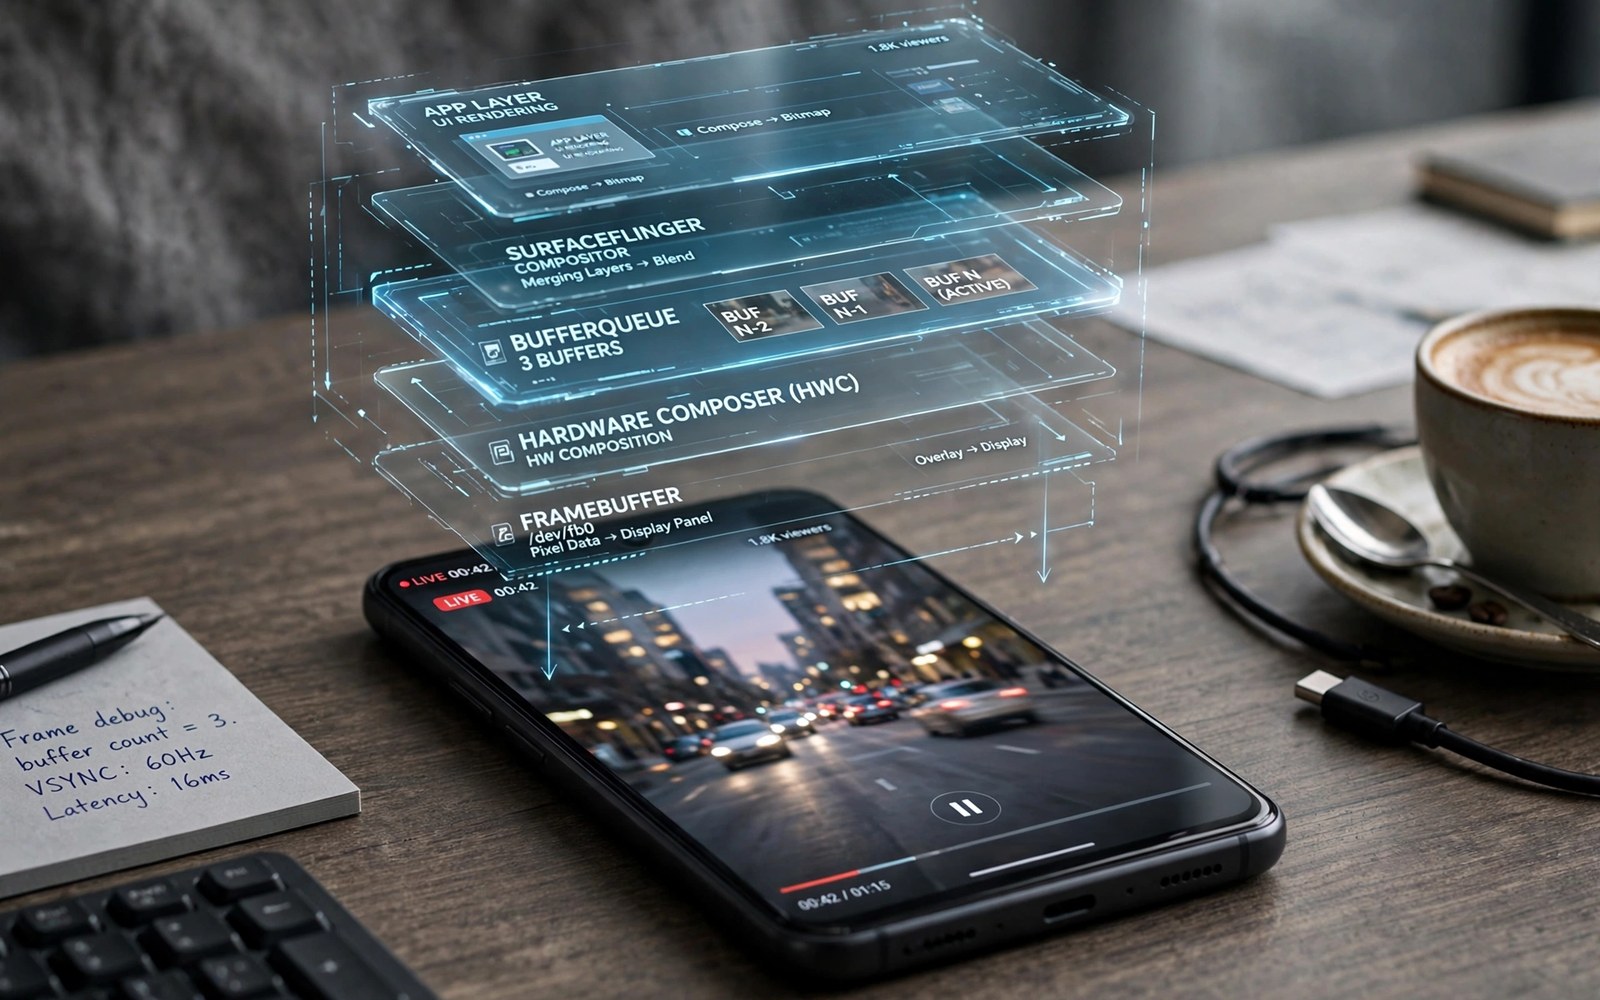
Implementing Dynamic Frame Buffer Swapping for Live Stream Injection
Live video injection fails quietly when the buffer pipeline is wrong. The stream keeps running, the app reports no error, and the viewer sees torn frames or frozen motion. I learned this the hard way on a virtual camera project where the video looked fine in a five-minute test and fell apart in a forty-minute call. The cause was a swap that happened a few milliseconds too late, and the fix was a clear mental model of how buffers move between producer and consumer.
This guide builds that model step by step and stays practical throughout. You will learn how double and triple buffering behave under real load, which components own each job, how to choose a swap point that never corrupts a visible frame, and how to test the pipeline on real hardware. Every section adds one layer of detail without changing the core idea: a swap must happen before the consumer locks the buffer for display.
How Dynamic Frame Buffer Swapping Works in a Live Stream
A frame buffer is a block of memory that holds one complete video frame. The producer writes pixels into a buffer, the consumer reads those pixels and sends them to the display or the encoder, and the swap decides which buffer is current. Dynamic frame buffer swapping replaces the contents of the buffer that is about to be displayed so a live stream can carry new video without rebuilding the pipeline. The swap itself is cheap; the timing around it is everything.
Think of it as a relay. The producer fills buffer B while the consumer shows buffer A. When B is complete, the two buffers change roles at a defined safe point. The consumer never reads a buffer that is still being written, and the producer never writes into a buffer that is still on screen. When that rule holds, the viewer sees smooth motion. When it breaks, the viewer sees half of one frame and half of another.
Double Buffering Basics for Live Video
Double buffering uses two buffers and alternates between them. It is the simplest design that works, and it is the right starting point for most live stream injection projects. The producer writes into the spare buffer while the consumer reads the current one, and the swap exchanges their roles. A developer who recognises this pattern can adapt faster to a new phone or a new release, because the pattern repeats across devices even when vendor details differ.
The limit of double buffering shows up when the producer is slower than the consumer. The consumer finishes reading and waits, or the producer overwrites a buffer that is still queued. Either way the stream stutters. That is the moment to consider a third buffer rather than to add locks and retries that hide the real problem.
Triple Buffering and the Latency Trade-Off
Triple buffering adds a third buffer so the producer always has a spare, even when the consumer is slow. It adds headroom, and that headroom smooths out jitter when frame production time varies. The cost is latency: a frame can sit in the queue one cycle longer before it reaches the screen, and viewers may notice the delay in a two-way call.
For a one-way broadcast, the extra latency rarely matters. For a live call where lip sync and reaction time matter, it does. Measure the added delay on your target device before you commit to triple buffering, and keep the queue depth configurable so you can tune it per device instead of hard-coding it.
Where the Swap Happens in the Pipeline
The safest swap point is the moment a fresh frame is queued and the old frame is done. In practice that means the swap happens inside the consumer’s vsync or frame-ready callback, never in the middle of a producer write. Put the swap logic in one place, guard it with a single check, and log every swap that gets skipped because the next buffer was locked. Those skipped swaps are the earliest warning that your timing is wrong.
Why the Consumer Must Never Read a Buffer Being Written
A torn frame is the visible result of a read racing a write. The top half of the screen shows the old frame and the bottom half shows the new one, and the viewer notices at once. The fix is not a faster write; it is a rule that the producer cannot touch a buffer once it has been handed to the consumer. Enforce that rule with ownership flags, not with comments in the code, because ownership flags fail loudly when they are violated.
Core Components of a Frame Buffer Swap Pipeline
The system breaks into a small set of components that each own one job. Clear ownership makes faults easier to locate when a session fails, and it keeps interfaces between components narrow so a change in one place does not ripple everywhere. Six pieces cover the whole design.
- Producer buffer pool. A fixed set of buffers the producer cycles through. A fixed pool bounds memory use and makes leaks visible at once.
- Consumer display queue. An ordered queue of buffers waiting to be shown. The queue depth sets the latency budget for the whole pipeline.
- Swap controller. The single place that decides when two buffers exchange roles. One controller means one place to debug when timing goes wrong.
- Timestamp store. A record of when each buffer was filled, so audio can stay matched to video frame by frame.
- Format descriptor. The width, height, pixel format, and stride of every buffer, checked at allocation time rather than at display time.
- Drop policy for stale frames. A rule that decides which frame to discard when the queue is full, so the stream stays live instead of falling further behind.
Each component can be tested alone before the full pipeline is assembled. Isolated tests catch format and timing faults early when they are cheap to fix, and they give you a known-good baseline to return to when integration gets messy.
Producer Buffer Pool: Fixed Size, Clear Ownership
Allocate a small pool of buffers at startup and never grow it during a session. A pool that grows without a limit wastes memory, and a pool that shrinks mid-session creates allocation pauses at the worst moment. Three buffers suit most live streams; four helps when the producer is bursty. Test both sizes on your slowest target device and keep the number that holds a steady frame rate.
Consumer Display Queue: Depth Sets Latency
The display queue holds finished buffers in order. A queue of one keeps latency lowest and risks a dropped frame when the producer hiccups. A queue of three absorbs hiccups and adds a frame or two of delay. For live injection, start with a depth of two and adjust only after measuring real sessions. Readers who want a related view can explore How Application Sandbox Isolation Fights Framework Level API Interception for more context on how the Android sandbox shapes what a pipeline can touch.
Swap Controller and Timestamp Store
The swap controller is the only component allowed to change which buffer is current. It checks that the next buffer is complete and free, attaches the timestamp, and then performs the exchange. The timestamp store travels with each buffer so the audio path can match sound to the exact frame on screen. Timestamps must travel with the buffer or audio will drift away from video, and the drift grows slowly enough that a short test will miss it. Test with a thirty-minute session, not a thirty-second one.
Format Descriptor and Drop Policy
The format descriptor records width, height, pixel format, and stride for every buffer, and the pipeline refuses a buffer whose descriptor does not match the negotiated format. That refusal is a feature: a mismatched format shown on screen is worse than a dropped frame. The drop policy decides what to discard when the queue fills. Drop the oldest frame when the queue is full, because the newest frame is the one the viewer needs right now. A policy written down and tested beats a policy improvised during a live session.
Design Choices That Shape Latency and Reliability
Every design choice trades simplicity against control and performance. A simple path is easier to maintain but it may hide options a power user needs. A flexible path offers control but it needs more tests and more documentation. Choose the simplest design that meets the stated requirement, and add complexity only after a real test shows the simple design falling short.
Three choices dominate the outcome. First, the queue depth, which sets latency. Second, the drop policy, which sets how the pipeline behaves under overload. Third, the timestamp strategy, which sets whether audio and video stay matched over a long session. Get those three right and most other details become easy.
Timestamps Travel With Every Buffer
Attach a timestamp to every swapped buffer at the moment the producer finishes writing it. Use a monotonic clock such as System.nanoTime() so the value never jumps backwards when the wall clock changes. The consumer compares the buffer timestamp with the audio clock and adjusts presentation timing when the gap grows. See also Manipulating Audio Input Formats (PCM, AAC) via Framework Hooks for a related perspective on how audio timing interacts with the video path.
Bounded Queues Stop Memory Growth
A queue with a clear capacity limit prevents memory growth during a stall. When the producer outruns the consumer, the queue fills and the drop policy takes over. Without a limit, a stalled consumer lets the queue grow until the process runs out of memory, and the crash log will blame the wrong component. Set the limit at allocation time, log every drop, and treat a rising drop count as a signal to investigate rather than as normal behaviour.
When to Add Complexity to the Design
Add a third buffer when double buffering drops frames on your slowest device. Add a jitter buffer when network timing varies. Add a fallback path when a device lacks a hardware feature you depend on. Each addition earns its place only after a real test shows the simpler design failing, and each addition gets its own test so you can remove it later if the need disappears.
Implementation Steps for Dynamic Frame Buffer Swapping
Work through the steps in order and verify each step before moving on. Early verification saves time because a fault found late is harder to trace, and a pipeline built in verified layers is easier to debug than one assembled all at once.
- Allocate a small pool of buffers at startup, with the format descriptor checked for every buffer before the session begins.
- Let the producer fill one buffer while the consumer reads another, and never allow both sides to touch the same buffer at the same time.
- Swap the active buffer only at a defined safe point, inside the consumer’s frame-ready callback, and only when the next buffer is complete and free.
- Attach a timestamp to every swapped buffer using a monotonic clock, and store it where the audio path can read it without locking.
- Drop the oldest frame when the queue is full, log the drop, and keep the newest frame for display.
- Measure swap latency during a real streaming session on real hardware, and record the numbers with the device model and Android version.
For a neighbouring topic, see Android NDK C++ Code Interfacing with Java Framework via JNI and compare its approach with this one, especially where native code hands buffers to the Java framework. The boundary between native and managed code is where most buffer lifetime bugs hide.
A Small Swap Sketch to Start From
The snippet below is a sketch, not production code. Read it as a statement of the rule, then adapt names and error handling to the codebase where it will live.
FrameBuffer swap(FrameBuffer current, FrameBuffer next) { if (next == null || next.isLocked()) return current; next.setTimestamp(System.nanoTime()); return next; }
Three details matter in that sketch. First, the null check, because a missing buffer must never crash the stream. Second, the lock check, because a locked buffer must stay current until it is free. Third, the timestamp, because a swapped buffer without a timestamp will drift out of sync with audio. Add logging around the critical call so a failure leaves a clear trace, and keep the function short enough that a reviewer can see the whole rule at a glance.
Verifying Each Step Before Moving On
After allocation, confirm every buffer reports the negotiated format. After the first swap, confirm the consumer shows the new frame and the producer writes into the old one. After the first drop, confirm the log records it and the stream continues. These small checks take minutes and they catch the faults that cost hours when found late.
Performance and Reliability Testing on Real Hardware
Performance work starts with measurement rather than with guessing. Measure latency and throughput on a target device under realistic load, because a change that helps on one device can hurt on another device with a different chip. Testing at this stage should use real hardware rather than only an emulator, since real hardware reveals timing and format differences that an emulator hides.
Build a test matrix that covers a flagship, a mid-range phone, and a budget phone, each on the Android release your users actually run. Record swap latency, drop count, memory use, and battery drain for a thirty-minute session on each device. Keep those numbers with the change record so the next engineer can see what was measured and what was assumed.
Measure First, Optimise Second
Profile before optimising and keep the profile data with the change record. The slowest part of a swap pipeline is rarely the swap itself; it is usually a copy, a format conversion, or a lock held too long. A profile tells you which one, and it stops you from optimising the wrong thing. I once spent a day tuning swap timing when the real fault was a format conversion running on every frame. The profile found it in ten minutes.
Clean Shutdown and Recovery After an Error
Reliability also means clean shutdown and recovery after an error. A pipeline that recovers gracefully earns user trust over time, and a pipeline that leaks buffers on every restart earns the opposite. Test stopping mid-session and restarting at once, because that sequence often exposes leaks that a normal shutdown hides. Keep buffers small and queues bounded so a stall cannot grow without limit, and watch memory and battery during long sessions because both reveal hidden costs.
Battery and Memory During Long Sessions
Watch memory and battery during long sessions because both reveal hidden costs that a short test misses. A slow memory leak shows up as a rising baseline over thirty minutes. A battery drain shows up as heat and a falling charge rate. Both are cheaper to fix before release than after users report them.
Common Pitfalls That Corrupt Frames or Break Lip Sync
Most failures in this area come from a small set of repeated mistakes. Learning those mistakes in advance prevents long debugging sessions, and naming them in a code review checklist keeps them from returning.
- Swapping a buffer that is still in use corrupts the visible frame, and the corruption looks random because it depends on exact timing.
- Growing the pool without a limit wastes memory, and the waste shows up only in long sessions when it is hardest to debug.
- Dropping frames without a policy creates uneven motion, because the viewer sees a burst of smooth frames followed by a jump.
- Ignoring timestamps breaks lip sync over time, and the drift is slow enough that a short test will miss it entirely.
- Testing with still images hides timing faults, because a still image never exercises the swap path under load.
Swapping a Buffer Still in Use
The classic fault is a swap that fires while the consumer still holds the buffer. The fix is an ownership flag checked at the swap point, plus a log line when the swap is skipped. If your logs show skipped swaps, the timing is wrong and the fix belongs in the scheduling, not in the swap function.
Unbounded Pools and Missing Drop Policies
A pool that grows on demand feels flexible until a stall turns it into a memory leak. A missing drop policy feels simple until the queue fills and the pipeline has no rule for what to discard. Write both limits down before you write the code, and test them by deliberately stalling the consumer for ten seconds.
Testing With Still Images Hides Timing Faults
A still image never changes, so a broken swap still looks correct. Test with moving video, with audio, and with a real network or encoder downstream. Recorded sessions and device logs give a better picture than invented examples, and keeping those test assets with the project lets a later change be checked against them.
Practical Walkthrough: From First Sketch to a Working Pipeline
Imagine a developer who starts a new project based on frame buffer swapping. The first task is to write down the expected input and the expected output in plain language. That written expectation becomes the test that later code must pass, and without it the developer cannot tell whether a change helped or harmed the result.
The developer then builds the smallest version that can run end to end. A small version exposes integration faults while the code is still easy to change, and each new feature joins only after the small version passes its basic tests. This discipline keeps the project moving even when a vendor detail surprises the team.
Write the Expectation Before the Code
Write down the frame rate, the resolution, the maximum acceptable latency, and the behaviour when the producer stalls. Those four numbers define the test, and the test defines whether the implementation is done. A project without those numbers drifts, because every change looks reasonable in isolation.
Build the Smallest End-to-End Version
Start with double buffering, a fixed pool of three buffers, a drop-oldest policy, and timestamps on every frame. Run it for thirty minutes on a real phone with audio. When that version holds steady, add one feature at a time and re-run the same test. The test stays constant while the code changes, and that constancy is what makes the results trustworthy.
Add Realistic Data and Timing
Next the developer adds realistic data and realistic timing to the test. Synthetic data that is too clean hides faults that real users will meet at once, so use recorded sessions and device logs. Keep those test assets with the project so a later change can be checked against them, and update them when the product changes.
Compatibility Across Android Devices and Releases
Android devices differ in chip and camera and audio hardware. A design that works on a flagship phone may fail on a budget phone with less memory, and budget devices often expose format limits that flagship devices hide. Test on low end hardware early because it reveals assumptions about speed and capacity that a flagship never challenges.
Vendor customisation adds another layer of difference across devices. Two phones on the same Android release can behave differently in edge cases, and Android releases also change behaviour over time. A path that worked on one release may need a new permission or a new service type later, so track release notes for the areas this project touches and update the test matrix when a new major release reaches users.
Budget Hardware Exposes Hidden Assumptions
A budget phone with 3 GB of RAM and a slower GPU will punish an unbounded pool and a careless format conversion. Run the full test matrix on the cheapest device you support, not just on the phone on your desk. The faults you find there are the faults your users will find first.
Vendor Customisation and Release Changes
Read vendor notes where they exist and keep a device specific note file. That file saves hours when a fault appears only on one model, because it records which devices need which workaround and why. Update it every time a vendor quirk costs you a debugging session.
Keep a Device-Specific Note File
One short file per device family, listing the model, the Android version, the quirks found, and the workaround used. Future readers need the reason behind a workaround to judge whether it still applies, and a note file is cheaper than rediscovering the same quirk twice.
Security and Privacy in Camera and Audio Pipelines
Camera and audio features touch sensitive data so privacy must be part of the design. Request only the permissions that the feature truly needs, and explain to users why each permission is needed in plain language. A clear explanation builds trust and reduces permission refusals.
Store captured data only for as long as the feature requires it. Delete temporary frames and samples promptly when a session ends, and encrypt stored media when the app keeps it beyond a single session. These habits limit harm if a device is lost or an account is compromised.
Permissions and Data Retention
Ask for camera and microphone access at the moment the feature needs them, not at first launch. A permission requested in context is granted more often and understood better. Set a retention limit in code, not in a comment, so temporary frames are deleted even when the happy path is interrupted.
Review Third-Party Code With the Same Care
Review third party code that touches the pipeline with the same care as first party code. A library can introduce a broad permission or a network call that the app did not intend, so keep the dependency list short and review updates before adopting them. Security work is ongoing and it rewards steady attention.
Frequently Asked Questions About Frame Buffer Swapping
What happens if a swap occurs while the consumer is still reading the buffer?
The visible frame tears: the top shows the old frame and the bottom shows the new one. The swap controller must check the lock flag and skip the swap when the buffer is still in use, then log the skip. A rising count of skipped swaps means the scheduling is wrong and the fix belongs in the timing, not in the swap function.
How do I keep audio and video in sync during a swap?
Attach a monotonic timestamp to every buffer at the moment the producer finishes writing it, and let the audio path compare that timestamp with its own clock. When the gap grows, the consumer adjusts presentation timing. Test sync over a thirty-minute session, because drift builds slowly and a short test will miss it. A related discussion appears in Virtual Camera Synchronization: Audio and Video Frame Match Strategies which covers a close subject in more depth.
Why does triple buffering add latency to a live stream?
A third buffer gives the producer a spare, so a finished frame can wait one extra cycle before the consumer shows it. That waiting time is latency. For a one-way broadcast it rarely matters, but for a two-way call it adds to the delay between speaking and being seen. Keep the queue depth configurable so you can tune it per device.
Can I test frame buffer swapping on an emulator alone?
No. An emulator hides timing faults, format limits, and vendor behaviour that real hardware exposes. Use the emulator for logic checks, then run every timing test on real phones, including a budget model. The cheapest device in your test matrix usually finds the faults first.
A solid implementation starts with a clear model and ends with honest testing. Shortcuts at the start usually return as faults later in the project, so take the time to verify formats and timing before promising a feature to users. Keep the design narrow and the logs clear, and build the next feature on a pipeline that already proves itself in daily use. Your concrete next step is to write down the four numbers for your project — frame rate, resolution, maximum latency, and stall behaviour — then build the smallest double-buffered version and run it for thirty minutes on a real phone.

