

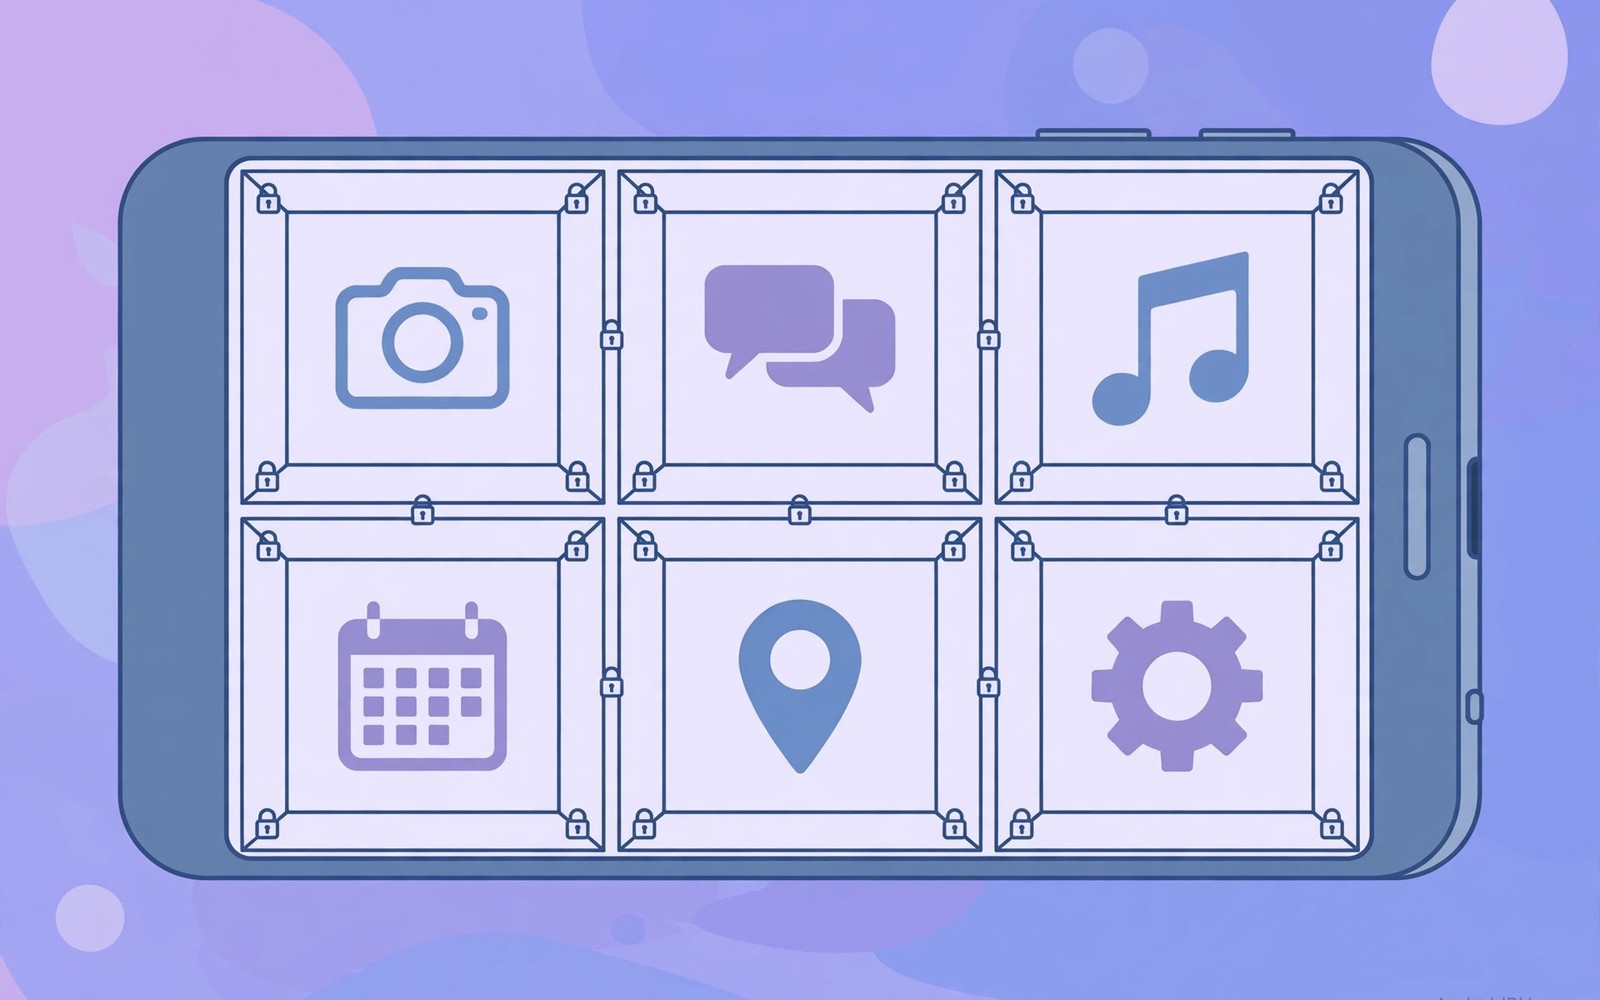
Android gives each app its own private space. That space is called a sandbox. Apps inside a sandbox cannot read each other files freely. The design limits damage from a single bad app. This guide explains how the sandbox works.
It covers user IDs and permissions and storage rules. It also covers the limits of sandbox protection. Readers who audit app behaviour can pair this with spotting risky apps for practical checks.
One App One Private Space
Android assigns each app a unique user ID. That ID owns the app private files. Other apps cannot open those files normally. The operating system enforces the boundary. A bad app faces the same wall as a good app.
The sandbox also separates app processes in memory. One app cannot read another app live memory. Crashes in one app rarely affect others. That isolation improves stability as well as safety. It forms the base of Android security.
Permissions Gate Cross-App Access
Permissions control access to shared resources. Camera and microphone and location need grants. Contacts and SMS need explicit approval too. An app without a grant cannot use the resource. Users can revoke grants at any time.
Some permissions allow narrow sharing between apps. A photo picker shares one image without full library access. A share sheet sends content only when you choose it. Those narrow paths replace broad access. They keep the sandbox strong while staying useful.
Scoped Storage Limits File Browsing
Scoped storage limits apps to their own folders. Apps need special approval for broad file access. Media access uses narrow photo and video scopes. That design stops casual snooping through files. A flashlight app cannot browse your documents.
File managers may request broader access for their job. Grant broad access only to tools you trust deeply. Review those grants in the permission manager. Revoke broad access when the job ends. Broad access is a privilege rather than a default.
- Each app gets a unique user ID.
- Private files stay outside other apps reach.
- Permissions gate cameras and sensors.
- Scoped storage limits file browsing.
- Share sheets pass only chosen content.
System Enforcement Layers
SELinux policies add mandatory access rules. Those rules bind even privileged system processes. A compromised process still faces policy limits. Kernel controls enforce the rules at a low level. Attackers must defeat several layers at once.
App signing ties updates to the original developer. A different signer cannot update an existing app. That rule blocks impostor updates through normal paths. It also supports safe sharing between same-developer apps. Shared signatures still respect permission grants.
Sandbox layers
App user ID: private files
Permissions: shared resources gated
Scoped storage: file browsing limited
SELinux: mandatory policy rules
Signing: updates tied to developer
Where The Sandbox Ends
The sandbox does not stop user-approved sharing. A user can grant contacts to a bad app. A user can paste a password into a fake app. Social tricks bypass technical walls easily. Careful grants matter as much as the sandbox.
Side channels can leak small hints across apps. Battery and timing signals may reveal activity. Those leaks rarely expose full file contents. They still matter for high-risk users. Keep risky apps off sensitive devices entirely.
Sandbox Habits For Users
Deny permissions that do not match app purpose. Prefer pickers and share sheets over broad grants. Remove apps that demand broad file access. Check special access grants every few months. A short review keeps the sandbox effective.
Use work profiles to separate sensitive apps further. Profiles add another sandbox boundary on supported phones. Banking apps inside a profile face fewer neighbours. That separation suits work and money tasks well. Combine profiles with strong locks for best effect.
The sandbox is Android quiet safety foundation. Unique IDs and permissions and storage rules work together. System policies add enforcement beneath app code. User grants remain the weakest point in the chain. Careful grants keep the sandbox doing its job.
Sandbox Design Trade-offs
Sandbox strictness trades against app convenience often. Strict sandboxes break features users expect. Photo apps want broad library access. File managers want broad file access. Designers balance safety against usefulness. Narrow pickers preserve most usefulness safely. Pickers share chosen items without broad grants. That design is the modern compromise. Users should prefer picker-based flows. Broad grants should remain rare exceptions. Readers who want encryption context should study encryption basics beside sandbox rules. Encryption and sandboxing protect different layers together.
Cross-app communication needs controlled channels. Intents let apps request actions from others. A share intent sends content you chose. A view intent opens content in another app. Malicious intents can exploit poorly written receivers. Developers must validate intent data carefully. Users cannot fix developer validation flaws. Keeping apps updated patches intent flaws. Updated apps resist known intent attacks. Update habits support sandbox design indirectly.
Web content inside apps creates sandbox questions. WebViews render web pages inside apps. A WebView inherits app permissions partly. Malicious pages inside WebViews threaten app data. Developers must restrict WebView capabilities. Users should avoid in-app browsers for sensitive logins. Open sensitive pages in a full browser instead. Full browsers offer stronger isolation controls. That habit reduces WebView risk greatly. Small habits complement system design well.
Clipboard sharing crosses sandbox boundaries daily. Copied passwords sit in shared clipboard space. Any app with clipboard access can read them. Modern systems warn about clipboard reads. Heed clipboard warnings for sensitive copies. Clear the clipboard after copying passwords. Password managers offer autofill instead of copying. Autofill avoids clipboard exposure entirely. Prefer autofill for all sensitive logins. Clipboard hygiene is sandbox hygiene too.
Sandbox Limits And User Responsibility
Sandboxing cannot judge user intent at all. A user may grant contacts to a bad app. The system honours explicit user grants. Grants override sandbox defaults by design. Careful grants are therefore essential. Review grants with app purpose in mind. Deny grants that purpose cannot justify. Revoke grants after one-time tasks end. Grant discipline is user sandbox maintenance. No system replaces thoughtful grants.
Accessibility services bypass many sandbox limits. Accessibility tools read screens for disabled users. Malicious apps abuse accessibility access heavily. Grant accessibility only to trusted tools. Question games requesting accessibility access. Question utilities requesting it without need. Accessibility grants deserve the highest scrutiny. Review accessibility grants quarterly. Remove grants for unused tools promptly. A single bad accessibility grant is dangerous.
Device admin grants also bypass sandbox limits. Admin apps can enforce policies and wipe data. Malicious admin apps resist removal strongly. Grant admin rights only to known tools. Work management tools are legitimate examples. Security tools may need admin rights too. Games never need admin rights at all. Deny admin requests from casual apps. An app demanding admin access is suspect. Find alternatives that work without admin power.
Backup and sync services move data outside sandboxes. Synced data leaves device sandbox protection. Account security then guards synced copies. Review sync settings for sensitive apps. Exclude sensitive apps from cloud sync. Local encrypted archives suit sensitive data. Archives need strong passwords and safe storage. Sync convenience trades against sandbox strength. Choose sync scope deliberately per app. Deliberate choices beat default acceptance always.
Sandbox Research And Future Directions
Sandbox research explores finer isolation levels. Future sandboxes may isolate features within apps. Feature isolation limits breach blast radius. A breached feature cannot reach other features. Finer isolation improves security granularity. Granularity trades against performance overhead. Overhead improvements enable finer designs. Research balances granularity against speed. Users benefit through updates eventually. Updates deliver research gains silently. Readers who audit app listings should also use spotting risky apps beside sandbox knowledge. Knowledge plus habits beats knowledge alone.
Machine learning aids sandbox policy generation. Learning systems suggest policies from behaviour. Suggested policies need human verification. Verification prevents over-permissive policies. Over-permissive policies defeat sandbox purposes. Human review remains essential for policies. Automation assists but never replaces judgement. Judgement understands context machines miss. Context includes user intent and purpose. Purpose-aware policies work best.
Hardware isolation complements software sandboxes. Secure enclaves isolate sensitive computations. Enclaves protect keys and biometrics strongly. Software sandboxes protect app data broadly. Hardware plus software layers reinforce. Reinforcement across layers resists diverse attacks. Diverse attacks need diverse defences. Single-layer defences fail eventually. Layered defences fail gracefully instead. Graceful failure limits breach impact.
Privacy sandboxes limit cross-app tracking. Tracking sandboxes restrict identifier sharing. Restricted identifiers reduce profiling accuracy. Profiling reduction protects user privacy. Advertisers resist restrictions naturally. Restrictions still advance through platform updates. Users benefit from default restrictions. Defaults matter more than optional controls. Optional controls go unused often. Default privacy protects passive users.
Developer education improves sandbox effectiveness. Developers must design for sandbox limits. Poor designs request broad permissions unnecessarily. Broad requests weaken user trust. Trust loss reduces app adoption. Good designs use narrow pickers. Narrow pickers preserve functionality safely. Education teaches narrow design patterns. Patterns spread through documentation and examples. Examples guide developers better than rules.
User education completes sandbox protection. Users must understand permission meanings. Meaningless permissions get granted blindly. Blind grants defeat sandbox purposes. Education explains permissions in plain terms. Plain terms improve grant decisions. Decisions improve with practice and feedback. Feedback comes from privacy dashboards. Dashboards show permission use history. History reveals overreaching apps clearly.
Sandbox Thinking For App Choices
Sandbox knowledge should guide app choices. Apps requesting broad access deserve scepticism. Scepticism is healthy for broad grants. Prefer apps using narrow pickers. Narrow pickers respect sandbox design. Respectful design signals developer care. Careful developers build safer apps. Safer apps deserve user trust. Trust should follow evidence not promises. Evidence includes permissions and behaviour.
The steps above follow the approach described in the official developer documentation for Android security and privacy. That documentation explains the same controls in general terms for phone owners who want a safer device.

